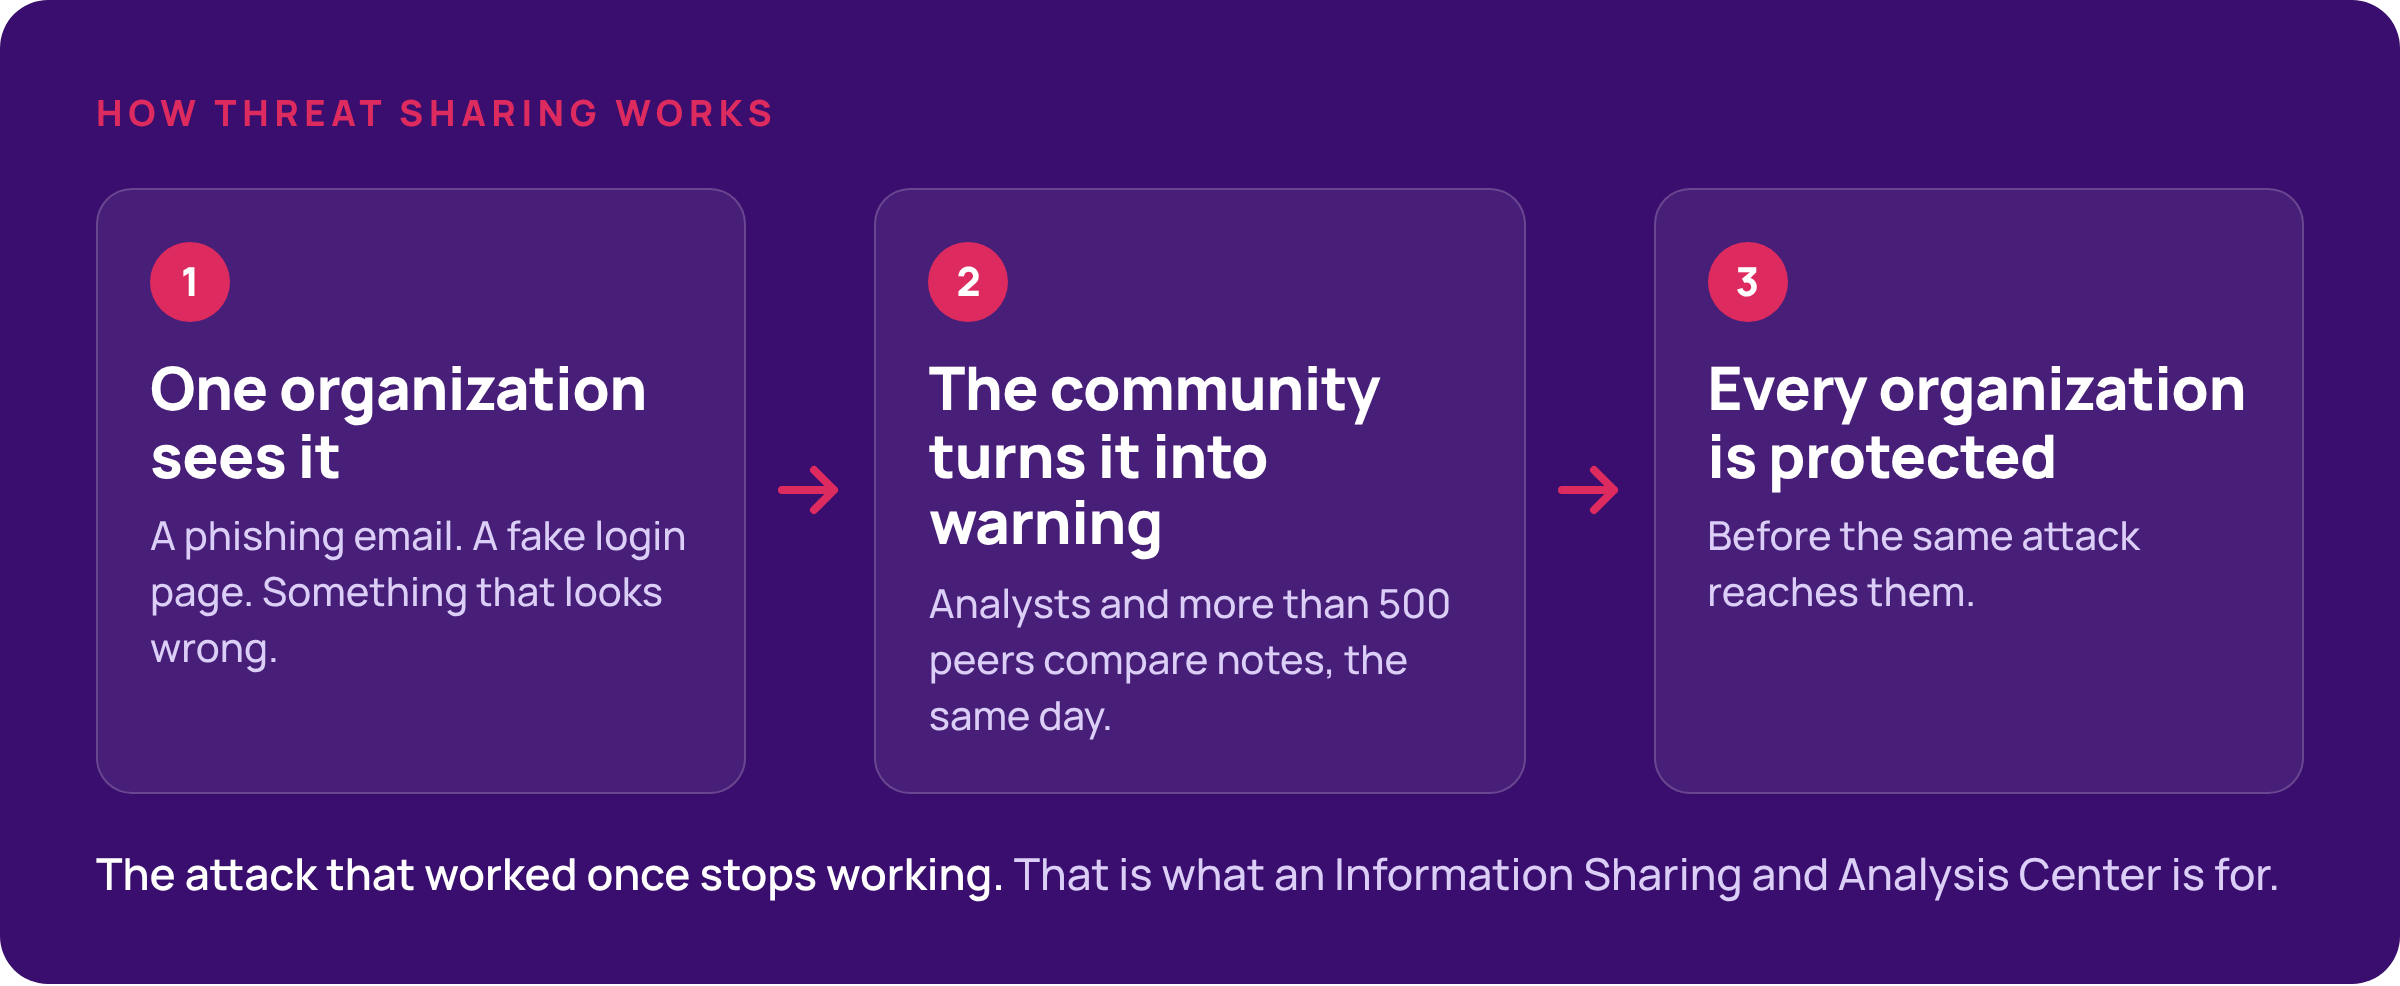
See it coming.The adversaries targeting civil society plan ahead. Our programs exist so the people defending it see what is coming, and are ready when it arrives. Why they existMost civil society organizations face serious digital threats with small security teams, or with no team at all: one person doing security alongside three other jobs. Everything we run is built for that person. It tells them what is coming before it arrives, and it helps them do something about it with the time and budget they have. Underneath all of it is one idea. A threat seen by one organization should protect every other organization. Members share what they see, the community turns it into warning for everyone, and the attack that worked once stops working.
What that means
Where this goesThe measure of this work is the attack that failed because someone saw it coming. The next step is reaching the organizations that have never had a security person and never will, and are targeted anyway, and bringing more of the people who see the most, in government and industry, into the room with the people who need them. No one protects civil society alone. |
NGO Information Sharing & Analysis Center
PO Box 150684 Alexandria, VA 22315 US© Copyright 2026. All rights reserved.
Privacy Policy